Aurialis Cyber Defence
A full Continuous Threat Exposure Management (CTEM) program and a managed Vulnerability Operations Center (VOC) the exposure management methodology and the operations center that runs it.
We cover the complete cycle:
Discover, prioritize by real-world exploitability, validate, and guide remediation, continuously across your external and internal attack surface, not a one-off scan.
One solution, two disciplines
A CTEM program and a VOC together
Most vendors sell you a platform and leave you to run it. Aurialis gives you both the methodology and the team that operates it.
CTEM
Continuous Threat Exposure Management: the complete five stage cycle that keeps your real exposure understood and shrinking over time, instead of a snapshot that’s stale the day after.
Managed VOC
A Vulnerability Operations Center that actually runs the cycle for you: discovering, prioritizing, validating, and driving remediation, so exposure is worked, not just displayed on a dashboard.
Continuous, not a one-off scan
We run every stage of the CTEM lifecycle on a loop, the two hardest stages, validation and mobilization, included.
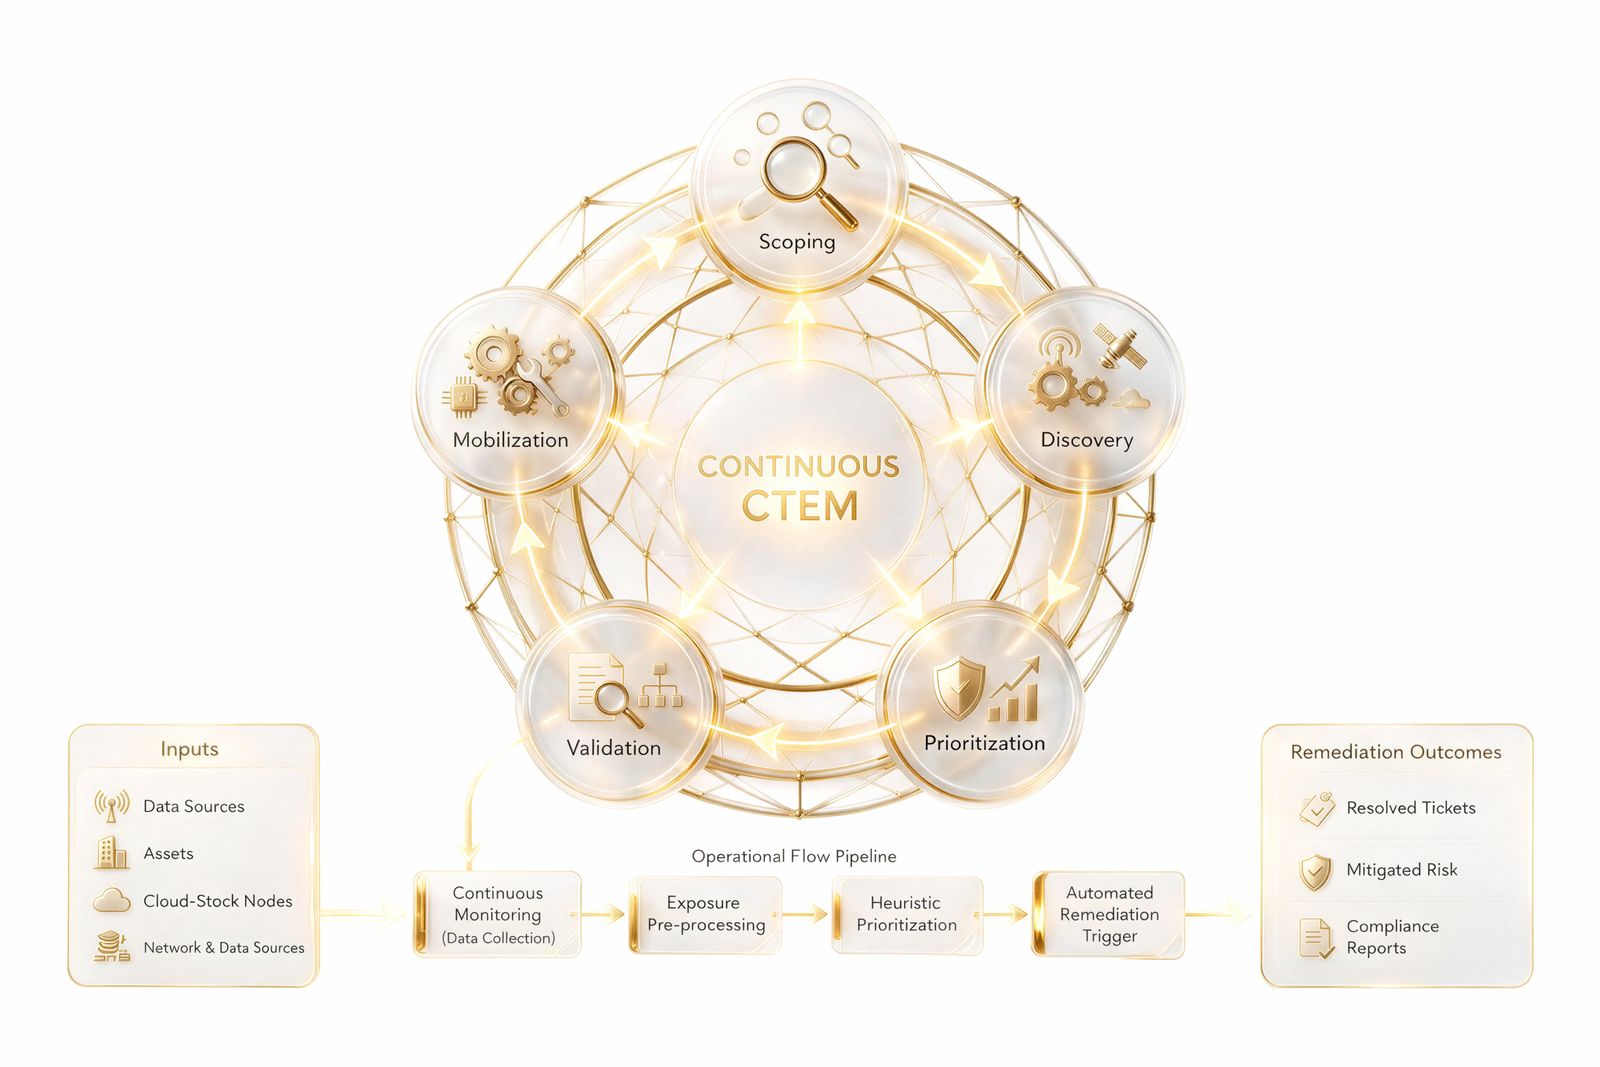
1 · Scoping
2 · Discovery
3 · Prioritization
4 · Validation
5 · Mobilization
One view of your real exposure
Internal, external, credential, and human exposure, unified, continuous, agentless where it matters.
External attack surface
Continuous discovery of internet-facing assets, misconfigurations, and exposures before attackers find them.
Internal, agentless
Assess internal weaknesses and verify control effectiveness, no agents to deploy across your estate.
Dark web & credentials
Monitor for leaked credentials and mentions of your organization surfacing across the dark web.
Human & social engineering
Test and reduce human exposure with phishing, smishing, and vishing simulations tied to real remediation.
Exploitability-based prioritization
Correlate findings across pillars to rank what an attacker could truly chain and exploit.
Validation & remediation
Confirm real exploitability and guide fixes to closure, exposure worked to resolution, not left on a list.
Managed, or your own team
Managed VOC
We operate the full CTEM cycle for you, end to end : discovery, exploitability-based prioritization, validation, and remediation guidance. You get outcomes, not another console to staff.
Platform access
Prefer to run it in-house? Your security team operates the platform directly, with our support.
Run a VOC pilot with us
Tell us about your attack surface and we’ll scope a focused pilot.
 English
 Français